Unused OAuth client secrets are automatically deleted after 90 days
docs.databricks.com databricks.com
This is what was read here when it was published. databricks.com no longer carries it in what it publishes now.
Aurekai listening
Listen to this summary
Original instrumental score; voice stays in front.
Ready to listen
This reads the text available on this page using your browser's voice. It is not a publisher-recorded narration; voice processing depends on your browser.Databricks now automatically deletes a service principal's OAuth client secret after 90 days without use, consistent with unused access token cleanup. If a deleted secret is still needed, create a new OAuth secret.
More ways to use this
Open on another device

Scan to open this page. Your saved notes and account access are not included.
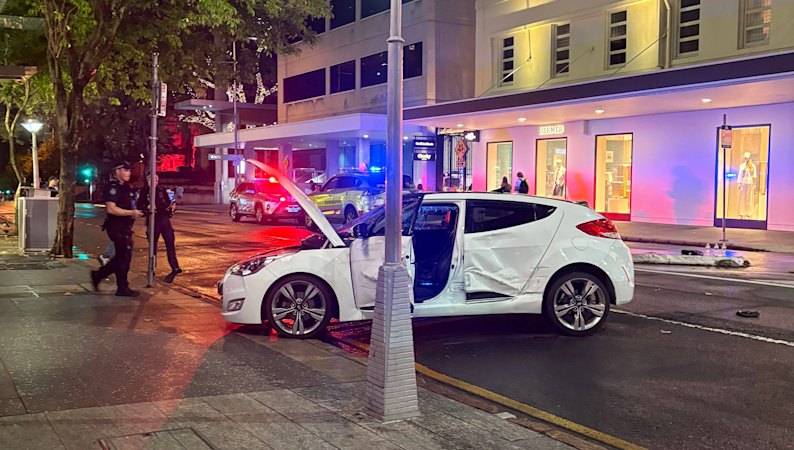 Car hits large group of people in Brisbane CBD after running red light
 Boy, 3, dies after being struck by ute at NSW holiday park
 U.S. urges critical infrastructure orgs to secure refrigeration systems ASAP after EU supermarket and blood bank attacks